Data Center Migration Guide for Secure Business Moves
A data center move can look straightforward on a project plan: relocate equipment, reconnect circuits, validate systems, and resume operations. In practice, a single undocumented application dependency, late carrier handoff, or failed backup restore can interrupt the systems your staff and customers depend on. This data center migration guide outlines how business leaders can plan a controlled move without treating uptime, security, or recoverability as assumptions.
Start With Business Risk, Not Equipment
A migration is not simply a facilities project. It is a business continuity event that affects applications, communications, security controls, employee productivity, and customer service. Before deciding what equipment will move or where workloads will land, identify what the organization cannot afford to lose.
That conversation should define each critical system’s recovery time objective (RTO) and recovery point objective (RPO). RTO establishes how long a system can be unavailable before the business is materially affected. RPO defines how much data loss is acceptable if recovery is required. A financial system may need a short RTO and near-zero data loss, while an archive server may tolerate a longer outage. Treating every workload as equally critical can make a migration unnecessarily expensive. Treating all workloads as low priority creates avoidable exposure.
Business leaders should also identify peak operating periods, contractual service commitments, regulatory requirements, and departments that need advance notice. For organizations handling protected health information, financial data, government contract information, or client records, the migration plan must preserve required security and access controls at every stage.
Build a Complete Migration Inventory
Many migration problems begin with incomplete documentation. Servers and network devices are visible. The dependencies around them are often not. A line-of-business application may rely on a legacy database, a specific firewall rule, a DNS record, a certificate, a shared file path, or an integration with a third-party service.
Create an inventory that documents hardware, virtual machines, operating systems, applications, databases, network configurations, storage, backup jobs, licenses, service accounts, and vendor contacts. Include ownership for each system. If no one can identify who validates an application after cutover, that application is not ready to move.
The inventory should also distinguish among workloads that will be physically moved, replicated to a new environment, retired, or replaced. This is where a migration can create real operational value. A business may find aging servers that are costly to move, unsupported operating systems that should be isolated or replaced, and underused workloads that are better suited to a hosted, colocation, or cloud environment.
Map Dependencies Before Scheduling Downtime
Dependency mapping turns an equipment list into a working plan. Document which applications communicate with each other, what ports and protocols they require, where their data resides, and how users access them. Include identity services, email relays, multifactor authentication, printing, voice systems, remote access, and monitoring tools.
Network dependencies deserve particular attention. A new data center may use different IP ranges, routing rules, internet providers, or firewall policies. If public-facing services are moving, plan DNS changes carefully and reduce time-to-live values in advance when appropriate. A DNS update alone does not guarantee that every external provider, user device, or application will immediately recognize the new destination.
Choose the Right Migration Method
The right method depends on the application, its downtime tolerance, available budget, and the target environment. A physical move may be practical for smaller, noncritical systems with tested backups and a clear maintenance window. It can also be the highest-risk option for aging hardware because transport, power changes, and reassembly may expose existing faults.
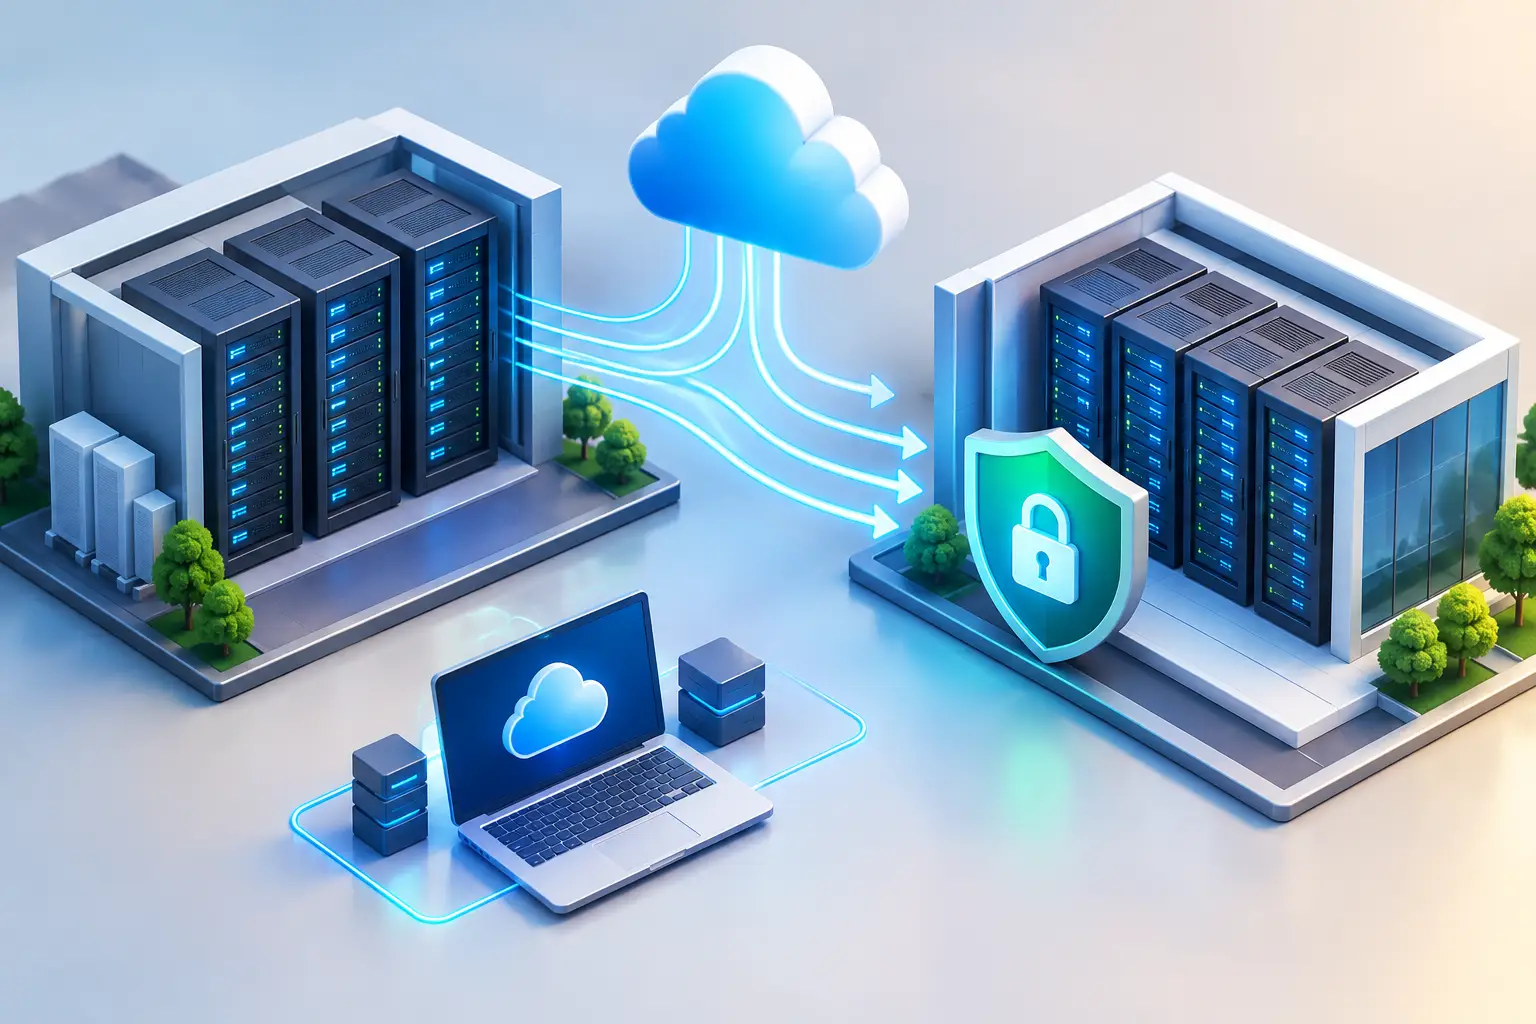
For critical virtual workloads, replication is often a safer approach. Data is copied to the destination in advance, synchronized repeatedly, and switched over during a planned window. This reduces the amount of data that must move during the outage, but it requires sufficient bandwidth, compatible platforms, and disciplined testing.
Some businesses use a staged approach. They migrate lower-risk services first, validate the new network and support processes, then move production workloads in planned waves. This extends the project timeline but lowers the chance that one issue affects every business system at once.
A move also presents a decision point: should the workload remain on owned infrastructure, move to a colocation facility, shift to managed hosting, or be redesigned for cloud infrastructure? There is no universal answer. Predictable workloads with specialized requirements may fit well in a professionally managed data center. Applications that need flexible capacity or geographic redundancy may benefit from cloud services. The key is selecting an environment that meets performance, security, cost, and recovery requirements over time.
Protect Data and Security Throughout the Move
Backups are necessary, but a backup job marked successful is not proof of recoverability. Before migration, verify that critical data can be restored and that recovered systems can actually operate. Test application-level recovery, not just file restoration. Confirm backup retention, encryption, offsite copies, and access controls.
Security controls must move with the workload. Review firewall rules, endpoint protection, logging, privileged accounts, vulnerability management, and alerting before cutover. A rushed migration can create temporary exceptions that remain in place for months, leaving broad access or unnecessary open ports behind.
Physical security matters as well. For equipment in transit, maintain chain-of-custody documentation, use appropriate packing and transport, and limit access to authorized personnel. At the destination, confirm rack security, power redundancy, environmental monitoring, visitor controls, and secure disposal procedures for retired hardware.
For many Washington, DC-area organizations, cybersecurity requirements also extend to customers, insurers, auditors, and contract partners. Documenting the migration process, validation results, and security decisions provides useful evidence that the organization managed the change responsibly.
Create a Cutover Plan With a Real Rollback Path
The cutover plan should be detailed enough that the technical team does not have to make high-impact decisions under pressure. It should identify the exact sequence of events, responsible individuals, communications procedures, validation tests, escalation contacts, and criteria for declaring success or initiating rollback.
Before the migration window, complete a readiness review covering at least these areas:
- Verified backups and documented restoration procedures
- Tested connectivity, power, cooling, and carrier circuits at the destination
- Approved firewall rules, VPN access, and monitoring configurations
- Named business owners available to validate critical applications
- A rollback plan with a defined decision deadline
The rollback plan is not a sign of poor preparation. It is an essential control. If the new environment fails validation, the team needs to know whether it can restore service at the original location, fail over to a recovery environment, or continue troubleshooting within an acceptable outage window. The answer changes by workload, which is why rollback decisions must be made before the migration begins.
Communication should be direct and specific. Tell employees what will be unavailable, when the maintenance window begins and ends, what workarounds are available, and where to report problems. Customers may need notice if external portals, phone systems, or service delivery will be affected.
Validate More Than Server Availability
A server that responds to a ping is not necessarily a functioning business service. After cutover, validate each system from the user and business-process perspective. Can authorized users sign in? Can they access the application remotely? Are transactions posting correctly? Are integrations, scheduled jobs, printing, scanning, voice services, and reporting operating as expected?
Technical validation should confirm performance, backup completion, security logging, monitoring alerts, patch status, and replication health. Compare baseline performance with the new environment. A migration may technically succeed while users experience unacceptable latency because a database, storage system, or network route was not sized correctly.
Keep the project team engaged after the first successful login. The first 24 to 72 hours often reveal permission issues, missed dependencies, certificate problems, and workflow gaps that were not visible during testing. Maintain a structured issue log, prioritize incidents by business impact, and document configuration changes made during stabilization.
Treat the Move as an Ongoing Operational Improvement
Once systems are stable, update network diagrams, asset records, disaster recovery documentation, support procedures, and vendor contacts. Review what caused delays, which assumptions were wrong, and where documentation was incomplete. Those lessons strengthen the next infrastructure change and improve the organization’s ability to recover from an unexpected event.
A well-managed migration should leave the business in a better position than before: clearer system ownership, stronger backup validation, better visibility, and infrastructure aligned with current needs. For organizations that need planning, hands-on execution, or continuing oversight, a partner such as CMA Technologies can provide accountable support across the migration lifecycle. The best next step is to define the systems your business cannot afford to lose, then build the migration plan around protecting them.